NL-SYS-03 full text
NL-03
NL EUDI Wallet Certification System
Organization and Support for the NL EUDI Certification System Owner
RC1.1
2026.10.31
| Document reference | NL-SYS-03 |
|---|---|
| Version | RC1.1 |
| Status | Release Candidate |
| Date | 31/10/2026 |
| Document type | Framework document |
| Parent framework | none |
| Scheme Owner | Kingdom of the Netherlands Minister of Economic Affairs |
| Certification target | European Digital Identity Wallets and the electronic identification scheme under which they are provided |
| Primary audience | System/Scheme Owner, CABs, EUDI Wallet providers, PID Provider |
| Secondary audience | EUDI Wallet ecosystem stakeholders |
| Assurance level <identity proofing CIR 2015/1502> and <evaluation, EU Regulation 2019/881> | High/High |
| Subsidiary Documents | NL-TL, NL-FS-, NL-CS-, NL-PW-* and NL-PP-* |
| History of changes - Version | History of changes - Change | History of changes - State | History of changes - Date |
|---|---|---|---|
| RC1.0 | First Consolidated Version following European Collaboration and Refinement Discussion with BZK- Policy Department and Legal. | Release Candidate | 2026-10-20 |
| RC1.1 | Release Candidate for publication following review round NL Certification System Mngt Board | Release Candidate | 2026-10-31 |
1 Scope
- 1 This document enumerates obligations and procedures of the System Owner & TopLevel Scheme Owner in relation to the NL EUDI Wallet certification system.
- 2 Additionally, the role of Supervisory Body in surveillance of the Trust Framework is described given its strong influence on risks to the EUDI Wallet related services which are subject to certification.
- 3 For The Netherlands, the System Owner & Top-Level Scheme Owner will be the Minister of Economic Affairs.
- 4 Currently, the scope of this document covers supervising the application and maintenance obligations for the the certification (schemes) for Wallet Providers and PID Providers ().
2 Legal and normative documents
- 7 In order to carry out certification of European Digital Identity Wallets, a certification system is established regarding compliance with Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014 as regards establishing the European Digital Identity Framework on the basis of ISO/IEC 17067 and ISO/IEC 17065 standards and operated under the accreditation system as described in Regulation 765/2008.
- 8 The EUDI Wallet certification system and its schemes demonstrate compliance with the following legal instruments:
- I. Functional framework Article 5a of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014and respective Commission Implementing Regulations:
- EU 2024/2977
- EU 2024/2979
- EU 2024/2980
- EU 2024/2982
- II. Certification Rules (Article 5c, 45a (4) of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014) and the Commission Implementing Regulation EU 2024/2981
- III. European Cybersecurity Certification EUCC program EUCC as defined in the Commission Implementing Regulation (EU) 2024/482
- IV. Articles 58-59 of Regulation (EU) 2019/881 Cybersecurity Act
- V. Article 8(3) of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014on eID and trust services for electronic transactions along with Commission Implementing Regulation (EU) 2015/1502
- 9 In addition, the EUDI Wallet Certification System will comply with:
- I. [Placeholder for references to NL national law when available]
3 Governance and System / Scheme Management
3.1 Ministry of Digital Affairs governance arrangements
- 9 The System and Top-level Scheme Owner role is assigned to Minister of Economic Affairs that will govern these in close collaboration with the Minister of the Interior as with regard to the specificities of the NL National eID Scheme .
- 10 For practical maintenance of the system, the Minister will be supported by a “NL EUDIW Certification System Management Board” that consist of representatives of these respective government actors, as well as government-designated actors on Certification, Accreditation, Supervision, Cyber Resilience and Dutch Law.
3.2 Maintenance processes and review procedures
- 11 The System and Top-Level Scheme Owner shall ensure the continuous alignment of the NL EUDI Wallet Certification System with the requirements established under Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014, the related Commission Implementing Regulations, and optionally the Architecture and Reference Framework (ARF).
- 12 The System and Top-Level Scheme Owner shall maintain the scheme by establishing and implementing ongoing monitoring of developments within the European Digital Identity Wallet ecosystem, such as amendments to legislation, technical specifications, and interoperability requirements.
- 13 Whenever changes to the Union regulatory or technical framework or any other material change to the scheme occur, the System and Top-Level Scheme Owner shall assess their relevance and, where necessary, update governance arrangements, the scheme documentation, and operational procedures to maintain full consistency with applicable requirements.
- 14 To keep the NL EUDI Wallet certification System and related schemes aligned, the System and Top-Level Scheme Owner shall integrate information derived from certification, notification, monitoring activities, and statistical reporting to ensure the continued security, trust, and interoperability of the system and scheme.
- 15 Regardless of the reviews which are triggered ad-hoc by significant technical or regulatory updates, the System and Top-Level Scheme Owner shall establish, implement and operate the review procedure conducted on a periodic basis and thereby guarantee sustained compliance throughout the entire operational lifecycle of the scheme.
- 16 For changes to the scheme resulted from security incidents or handling of vulnerabilities – see Chapter 4.
3.3 Harmonization of the System and Scheme
3.3.1 Opinions and Recommendations
- 16 According to art. 5c(4) of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014, the System Owner shall transmit the draft national certification schemes to the European Digital Identity Cooperation Group whereby the Cooperation Group may issue opinions and recommendations.
3.3.2 Review by Certification System Collaboration Group
- 18 The EUDIW Certification System Collaboration Group was established to support cooperation among national authorities, national certification scheme owners, supervisory authorities and other competent organizations involved in the certification of the European Digital Identity Wallet (EUDIW).
- 19 In light of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014 and the implementing acts related to the European Digital Identity Wallet, the Group was set up to contribute to the establishment, maintenance and continuous improvement of a harmonized European framework for high assurance certification of EUDIW solutions.
- 20 The Group targets to be an experienced and competent Collaboration Group with the objective to foster cooperation, information exchange, mutual assistance and development of common practices among its members.
- 21 The Group targets to facilitate the exchange of views, promotes common interpretations of requirements, supports the development of harmonized evaluation methodologies, and seeks alignment of certification approaches across Member States. As an extension of this, the group targets that all this will allow also for a smooth transition towards harmonized EUDIW European Certification Schemes.
- 22 The end-objective of the Group is to ensure a harmonized high level of assurance of the European Digital Identity Wallet throughout Europe, fostering mutual trust, interoperability and consistent confidence in certified wallet solutions.
- 23 As such the System and Top-Level Scheme Owner will discuss the NL EUDIW Certification System and NL EUDIW top-level Certification Scheme periodically with its peers in this Collaboration Group when relevant changes to legislation, threat landscape, technology or other important events or evolutions occur.
4 Technical Vulnerability Management
4.1 Technical Vulnerability Management: Support for handling technical vulnerabilities
- 30 NOTE 1: This high-level procedure relates to NL-P-P/W-series and more specifically the resilience and software development and vulnerability management requirements (which might be subcontracted to a wallet solution provider).
- 31 NOTE 2: The management of technical vulnerabilities is a critical component of the operational security framework for the EUDI Wallet Certification Scheme. In accordance with Commission Implementing Regulation (EU) 2024/2981 and the requirements of the NIS 2 Directive, this process establishes a formal, coordinated approach for identifying, analyzing, and remediating vulnerabilities across the scheme's lifecycle.
- 32 NOTE 3: The primary objective is to maintain a high security assurance level through continuous monitoring and transparent communication between the System Owner, Scheme Owner, CABsn the Wallet Provider, and relevant European supervisory bodies. The procedural workflow, as illustrated in Figure 2, defines the responsibilities for risk assessment, regulatory coordination, and the mandatory exchange of vulnerability information. This mechanism ensures that any identified technical weakness is
Figure 2 Technical Vulnerability Management
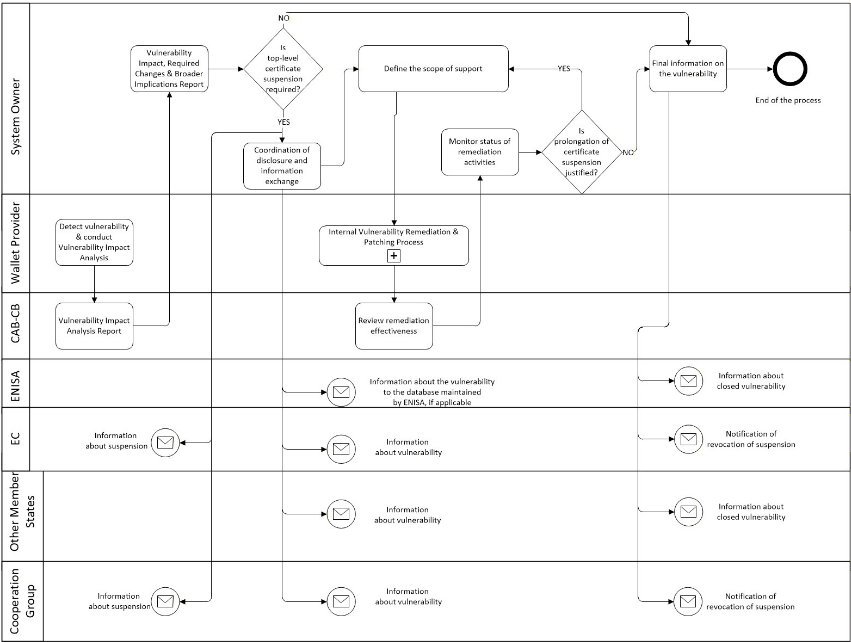
promptly addressed through internal remediation and patching by the Wallet Provider, while facilitating necessary disclosure to Member State authorities and the European Vulnerability Database maintained by ENISA, thereby preserving the integrity and trust of the EUDI Wallet ecosystem.
- 33 NOTE 4: The Scheme Owner is informed by the CAB-CB about the vulnerabilities based on Impact Analysis Report provided by the Wallet Provider. The information provided by the CAB-CB includes all elements necessary for the Scheme Owner to understand the impact of the vulnerability, the changes to be made to one or more elements of the EUDI Wallet Solution and, where available, any information from the CAB-CB on the broader implications of the vulnerability for other certified elements of the EUDI Wallet solution.
- 34 Upon receiving information about vulnerability and analyzing its impact and severity in relation to the certificate, and based on the decision of CAB-CB of suspension of the certificate, this is to be cascaded up to the top-level certificate and the NL EUDIW toplevel Certificate Scheme Owner shall notify the European Commission about this action according to the notification mechanism described in 7.1.2.
- 35 Additionally, the NL EUDIW top-level Certificate Scheme Owner shall share the relevant information about vulnerability with NL EUDI Certification System owner and the EUDI Wallet Certification System Collaboration Group, the EUDI Wallet Cooperation Group, ENISA, and with other Member States according to relevant mutual arrangements (in the extend that it is relevant or necessary).
- 36 The NL EUDIW top-level Certificate Scheme Owner shall monitor the status of remediation activities. It is upon the CAB decision to prolong the period of certificate suspension, if it is justified.
- 37 After the case is completed, the Top-Level Certificate Scheme Owner shall:
- notify the European Commission about changing the status of the top-level certificate,
- inform all relevant stakeholders accordingly.
- 38 In case the vulnerability is related to the component certified under the EUCC scheme, the provisions of Commission Implementing Regulation
- 39 NOTE: CIR 2024/482, chapter VI, “Vulnerability Management and Vulnerability Disclosure” apply. The Scheme Owner shall cooperate with the National Cybersecurity Certification Authority to handle the vulnerability.
5 Marks and Labels
5.1 EU DI Wallet Trust Mark
- 39 NOTE: EUDI Wallet Trust Mark is related to the top-level certificate issued under NL EUDI Wallet certification system according to the procedure specified in NL-TL.
- 40 In accordance with the Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014, users shall be provided with a clear means to verify that they are installing or, after activation, actively using a trusted and certified Wallet Solution.
- 41 To achieve compliance with this regulatory requirement, the Wallet Instance of the Provider’s Certified Wallet Solution shall incorporate a dedicated Trust Mark UI view. When a user invokes the Trust Mark within the Wallet Instance, the interface is specified to perform the following operations:
- Graphics Rendering: It renders the official Trust Mark graphics and/or logo.
- Informational Text Display: It displays informational text regarding the Wallet Solution certification, which must be localized according to the language settings of the user's device.
- Certification Connectivity: It provides web links directly to a list of certified Wallet Solutions, as well as to a specific web page containing the certification information of the user's active Wallet Solution.
- )
5.2 Mark of conformity under NL EUDI Wallet Certification Scheme
- 44 The NL EUDI Certification System shall establish an official mark of conformity that publicly attests successful evaluation and certification processes for relevant element of the Wallet solution under the NL EUDI Wallet certification system.
- 45 The System Owner shall grant Conformity Assessment Bodies (CABs) accredited by the Dutch Accreditation Body to perform certification in accordance with the NL-TS, NL-FS, NL-CS and NL-P-P/W-schemes the right to use the mark of conformity.
- 46 Conformity Assessment Bodies – Certification Bodies (CAB-CB) have the right to transfer this Trust Mark to holders of valid certificates issued under these schemes.
- 47 The System Owner shall maintain a register of entities which are entitled to use the mark of conformity, the associated certificates and their status of validity (current, suspended, revoked or expired).
5.3 Design and formats
-
48 The mark of conformity shall be presented under the following brand: “NL EUDI Wallet certification system”.
-
49 NOTE: Graphical presentation and rules for visual presentation are specified in a dedicated publication by the Minister of Economic Affairs.
-
50 The logo shall be complemented by an appropriate QR code that contains an URL to a portal hosted by the Certification System Owner (which will provide the required information as-well-as additional information about NL EUDI Wallet Certification System and top-level Scheme.
5.4 Rules for use the mark of conformity
- 52 The mark of conformity may be used only in the following cases:
- All information related to the NL EUDI Wallet certification system and top-level Certification Scheme issued and distributed by the System / Scheme Owner.
- Official documents issued by the CAB or the Scheme Owner, such as public reports, lists of certified products or services, statistical data and other public material related to the subject matter.
- Information platforms (websites, applications, portals dedicated to EUDI Wallet solution related services) linked to the certified product or service Provider, provided that clear indication of relevant certification is presented;
- Technical and commercial documentation of the European Certified Identity Wallet produced by the holder of certificate, including informational material, product specifications and presentations.
- 53 Any usage of conformity mark which is beyond the catalogue defined in the previous paragraph requires prior approval of the Scheme Owner.
- 54 The use of conformity mark is prohibited in the following cases:
- Including the mark of conformity in products, services or versions which are not included in the issued certificate.
- Modifying or combining the mark of conformity with trademarks or other logos,
- In relation with suspended, revoked or expired certificate which have been issued under NL EUDI Wallet certification system.
- 55 Any improper use of the will be subject to legal action taken.
6 Trust Framework
6.1 Supervision of Conformity Assessment Bodies
- 56 The Supervisory Body designated in accordance with the applicable national legal framework will be responsible for overseeing the activities of Conformity Assessment Bodies (CABs) that assess and certify products and services according to the NL wallet certification scheme and its subordinate schemes. [That means the following
requirements will be included in national law and replaced by a reference at that time:
- 57 The Supervisory Body shall ensure through both ex-ante and ex-post supervisory activities that CABs continuously comply with the applicable legal requirements, accreditation requirements, certification scheme requirements, and procedures governing the issuance, maintenance, suspension, and withdrawal of certificates.
- 58 The Supervisory Body shall perform its operational tasks including: o Monitoring the ongoing competence, impartiality, independence, and integrity of CABs,
o Reviewing certification processes, assessment methodologies, and certification decisions,
o Conducting both on-site inspections and off-site supervision of CAB activities and records.
- 59 The Supervisory Body shall verify that certificates are issued solely on the basis of sufficient, objective, and documented evidence demonstrating compliance with the applicable certification requirements and that certification decisions are taken in accordance with the rules of the relevant certification scheme.
- 60 The Supervisory Body is empowered to require CABs to provide all documentation, records, assessment reports, technical evidence, and certification decision records necessary to verify the correctness and consistency of certification activities.
- 61 The Supervisory Body shall investigate complaints, appeals, reports of irregularities, and indications of non-conforming certification activities and may perform targeted audits where there are reasonable grounds to question the validity of certification decisions.
- 62 Where deficiencies, procedural failures, or non-compliant certification practices are identified, the Supervisory Body may require the CAB to implement corrective actions within a specified timeframe and demonstrate the effective remediation of the identified shortcomings.
- 63 In cases where a CAB issues certificates without applying the required certification procedures, fails to maintain adequate evidence supporting certification decisions, or otherwise acts contrary to the applicable certification scheme, the Supervisory Body may order the suspension of the affected certification activities and require the review, suspension, or withdrawal of affected certificates where appropriate.
- 64 The Supervisory Body shall cooperate with accreditation bodies, competent authorities, and other supervisory authorities where necessary to ensure consistent oversight of certification activities and the integrity of the certification framework.
- 65 The Supervisory Body shall maintain records of supervisory activities and enforcement measures and shall prepare periodic reports on the performance of its supervisory
activities, including significant findings, corrective measures imposed, and actions taken to safeguard the reliability and credibility of the certification system.]
6.1 Supervision of European Digital Identity Wallets
- 66 The Supervisory Body designated in accordance with Article 46a (1) of Regulation (EU) 2014/910 as modified by Regulation 2024/1183 along with required contact details shall be appointed by national law.
- 67 According to Article 46a (3) of Regulation (EU) 2014/910, the Supervisory Body shall ensure through both ex-ante and ex-post supervisory activities that the providers and their wallets continuously satisfy the regulatory requirements, as well as through taking targeted enforcement actions when informed of any regulatory infringements.
- 68 The Supervisory Body shall perform its operational tasks including:
- Cross-border cooperation with other supervisory bodies,
- Requesting from the EUDI Wallet ecosystem stakeholders all necessary for compliance monitoring, o Conducting both on-site inspections and off-site supervision.
- 69 The Supervisory Body is empowered to demand that providers remedy any compliance failures and to suspend or cancel the registration of relying parties within the designated mechanism in cases of fraudulent or illegal wallet usage.
- 70 The Supervisory Body shall coordinate with the data protection authority any action regarding potential rule violations or data breaches.
- 71 In terms of incident response, the Supervisory Body shall report significant security breaches or integrity losses to the competent authorities and single points of contact and inform the public or require providers to do so if such disclosure serves the public interest.
- 72 In line with Article 46a (5) of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014, if a wallet provider fails to comply with a remediation demand within the timeframe specified by the authority, the Supervisory Body is empowered to order the suspension or complete cessation of the European Digital Identity Wallet provision, factoring in the severity, duration, and consequences of the failure. Such enforcement decisions shall be communicated without undue delay to the European Commission, the supervisory bodies of other Member States, relying parties, and the end-users.
- 73 As stipulated in Article 46a (6) and Article 46a (7) of the Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014, the Supervisory Body shall submit an annual report of its main activities from the preceding calendar year to the European Commission by March 31.
6.2 Trust Framework: Access & Registration Certificates
- 65 To establish a trust framework in the NL EUDI Wallet ecosystem, the
NL EUDIW Certification System Owner shall designate the Access Certificate Provider and the Provider of registration certificates related to Wallet & PID Provider to designated QTSPs.
- 66 These providers wil issue mentioned “certificates” to the PID Provider and Wallet Providers to to ensureauthenticity and validity during interactions of relying parties with Wallet Units.
- 67 These parties will be put on a designated TrustList by the NL EUDIW Certification System Owner. This registration will ensure their trust anchors (comprising public keys and unique identifiers) shall be published in a Trusted List by a designated Trusted List Provider. These lists are hence forward signed and made available through the Commission's List of Trusted Lists, enabling the verification of credentials across the ecosystem.
- 68 The Supervisory Body will be able to suspend or cancel registered Providers upon determining that specific regulatory conditions are not met.
6.3 Trust Framework: Registration of Wallet Providers
- 75 Following successful completion of relevant certification and additional evaluation processes and verification by the Supervisory Authority, the Wallet Providers will be recognized as a wallet provider in the NL Wallet eID Scheme and notified by NL to the EU to be put on a designated TrustList by the NL EUDIW Certification System Owner.
- 76 The Supervisory Body will also be able to suspend or cancel a registered Wallet Provider upon determining that specific regulatory conditions are not met.
- 77 Note: As a result of suspension or revocation, the status of the affected entity in the relevant Trusted List shall be changed to Invalid. Following this, all valid Wallet Unit Attestations (WUAs) associated with Wallet Units issued by that provider shall be revoked.
7 Reporting & Notification procedures
7.1 Notifications related to CABs to European COM
- 84 In accordance with Article 20(1b) of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014, Member States shall transmit to the European Commission the names, addresses and accreditation details of the Conformity Assessment Bodies (CABs) responsible for carrying out conformity assessments under the European Digital Identity Framework.
- 85 The information related to accredited and authorized CABs compliant to the Dutch Certification System and National EUDIW Certification Scheme will be communicated to the European Commission by the NL Certification System Owner.
- 89 This information to be included will contain:
- 90 (a) the name and address of the Conformity Assessment Body; $
- 91 (b) the accreditation details of the Conformity Assessment Body, including the scope for which the CAB has been accredited (and where applicable authorized);
- 92 (c) any modification of the accreditation status or accreditation scope of the Conformity Assessment Body that may affect its competence to perform conformity assessments under the European Digital Identity Framework;
- 93 (d) any withdrawal, suspension or termination of the accreditation or authorization of the Conformity Assessment Body relevant to its activities under the European Digital Identity Framework.
7.2 Notifications wrt Wallet and PID Providers to European COM
-
84 In accordance with Article 4 and Annex II of Regulation (EU) 2024/2980, the Member States shall transmit to the European Commission at least the detailed information for several category of service providers and in relation to this document information on the Wallet Providers and the PID Providers.
-
85 The information related to the certified and admitted Wallet Providers will be communicated by the Supervisory Authority (that is responsible for verifying certification and admission)”.
-
89 According to Article 3 of Commission Implementing Regulation (EU) 2024/2980 the Member State shall inform the European Commission about entities and mechanisms referred to in Article 5a (18) of Regulation (EU) 2024/1183 amending Regulation (EU) No 910/2014. In context of Certification of the PID-Provider and Wallet Providers this includes:
-
90 (b) the bodies responsible for the provision of European Digital Identity Wallets in accordance with Article 5a (1);
-
91 (c) the bodies responsible for ensuring that the person identification data is associated with the European Digital Identity Wallet in accordance with Article 5a (5), point (f);
-
92 (d) the mechanism allowing for the validation of the person identification data referred to in Article 5a (5), point (f), and of the identity of the relying parties;
-
93 (e) the mechanism by which to validate the authenticity and validity of European
Digital Identity Wallets.
7.3 Notifications of issues to European COM
- 101 NOTE: The lifecycle management of a Wallet Solution requires that the System Owner notifies the Commission to transition a Wallet Solution into a "Valid" state (i.e., certified). Furthermore, under specific regulatory conditions the status of certificate which is subject to notification can change It will call an action of an immediate update to the certificate register and corresponding notification to the Commission to maintain the integrity and trustworthiness of the EUDI Wallet ecosystem.
- 102 The Supervisory Authority (that is responsible for verifying certification and admission)”shall notify the Commission without undue delay regarding the certification of a Wallet Solution (i.e., the top-level certificate) as well as any subsequent expiration, suspension or revocation of such certification.
- 103 In the event of a suspension or revocation, the Supervisory Authority shall provide the underlying reasons for the decision to ensure regulatory transparency across the Union.
- 104 Notifications shall be transmitted in English via the secure electronic notification system. The Commission is entitled to request additional information or clarifications to verify the completeness and consistency of the notified data.
8 Complaint Handling
- 115 The complaint handling process serves as a structured mechanism for the Top-level, Functional, Cyber Security and Provider Scheme Owners to maintain effective oversight and ensure the accountability of the NL EUDI Wallet Certification Scheme. This procedure facilitates the formal intake, impartial investigation, and resolution of grievances, ensuring that all issues raised by stakeholders are addressed in a systematic manner.
- 116 The procedure commences with a registration of any complaint in the Complaint Management System hosted by the NL EUDIW Certification Scheme Owner and is followed by a formal analysis performed by the respective Scheme Owner upon receipt of a complaint. Should the submission contain formal deficiencies, the Scheme Owner initiates contact the Complainant to request necessary completions or clarifications. Once the application is complete, the Scheme Owner conducts a thorough substantive analysis to determine the scope and validity of the grievance.
- 117 During the investigative phase, the Scheme Owner acts as the central coordinator. Depending on the subject matter, the Scheme Owner may formally request the PID or EUDI Wallet Provider to submit evidence or technical statements related to the case. In instances involving complex technical inquiries, the Scheme Owner may also task the Conformity Assessment Body with providing expert documentation or an opinion regarding the wallet's compliance. Should the initial information prove insufficient to determine potential non-compliance, the Scheme Owner reserves the right to commission dedicated supervisory activities or seek the support of external independent experts at any stage of the process.
- 118 The final stage of the procedure involves the formal resolution and communication of findings. If a complaint is determined to be unfounded, the Scheme Owner issues a notification to the Complainant detailing the rationale for the resolution. If the complaint is found to be valid, the Scheme Owner notifies the Complainant, and, where appropriate, provides relevant information to the PID or EUDI Wallet Provider and the Conformity Assessment Body. Furthermore, in cases of confirmed nonconformity, the Scheme Owner formally notifies the Complainant, the Conformity Assessment Body, the PID or EUDI Wallet Provider, and the National Accreditation Body as well as the Supervisory Authority regarding the initiation of the nonconformity process. This ensures full traceability and adherence to certification oversight requirements, maintaining the integrity and trustworthiness of the national identity framework.
- 119 Where a complaint is lodged in accordance with Article 25 of the Act on the National Cybersecurity Certification System, the Scheme Owner shall cooperate with the National Cybersecurity Certification Authority and provide it with the information necessary to assess the complaint.
9 Secured Exchange of Information
- 121 The Scheme/System Owner, the EUDICG, the European Commission, CABs and all other stakeholders shall ensure the security and protection of trade secrets and other confidential information, including business secrets, as well as the preservation of intellectual property rights, All interested parties shall implement appropriate and compliant technical and organizational measures for protecting information.
- 124 The System Owner shall designate and adopt the cryptographic mechanisms specified in the relevant technical specifications referred to in the applicable regulations, in strict compliance with the security requirements stipulated in Annex I of Commission Implementing Regulation (EU) 2024/2979.
- 125 These mechanisms are mandated to ensure the security, integrity, and confidentiality of data exchanged within the EUDI Wallet ecosystem and shall be adhering to the common Union-wide cryptographic standards required for cross-border interoperability.
- 126 The System Owner shall maintain and disseminate an inventory of applicable cryptographic mechanisms and technical applications designated for use by Conformity Assessment Bodies (CABs) and Applicants.